About Author
Hannah Lloyd
Hannah Lloyd is CRO and co-founder of enhanced.io. She leads global new business generation and works directly with MSP partners to build and sell security practices.
enhanced.io, the channel-only Open XDR SOCaaS for MSPs
Here’s something that comes up in almost every partner conversation I have at the moment. A client goes through a cyber insurance renewal, or receives a security questionnaire from a much bigger customer, and suddenly they want to know who is watching their environment at 3am on a Sunday. They want the kind of security operations a large enterprise would have, and the MSP, quite reasonably, does not want to build a 24/7 security operations center from scratch to provide it.
What tends to happen next is a search for SOC-as-a-Service providers, and that’s where it gets a bit confusing, because a lot of the providers you’ll find were built to sell to large organizations directly, with the channel added on afterwards. To give you a bit of context on where I’m coming from: enhanced.io is a channel-only Open XDR SOCaaS built exclusively for MSPs, with 400+ integrations across endpoint, network, cloud, identity and IoT/OT. So I’ll be upfront that I have a view, and I’ll try to make this useful whichever provider you end up choosing.
In this piece I want to walk through what SOC-as-a-Service looks like operationally, what separates a provider built for the channel from one that tolerates it, and how to evaluate both. Does that make sense as a plan?
For context: enhanced.io ranked #88 in MSSP Alert’s 2025 Top 250 MSSPs, up from #106 in 2024.
What does SOC-as-a-Service include?
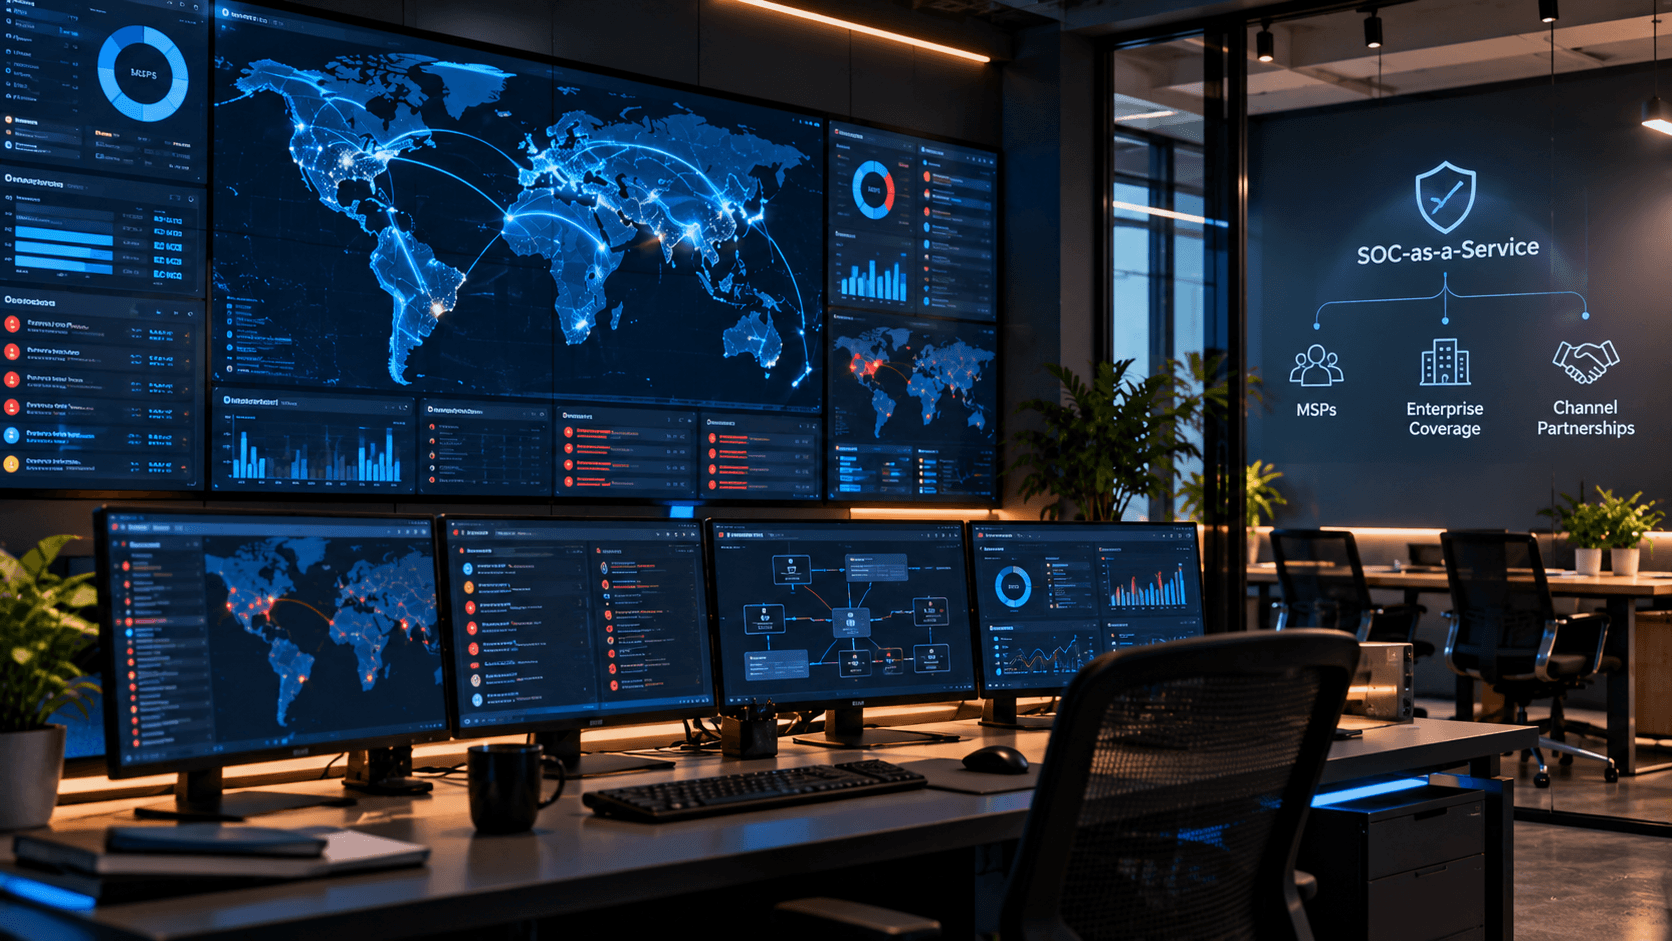
SOC-as-a-Service is a subscription security operations center. You get a team of analysts and the platform behind them, watching your clients’ environments around the clock, triaging what the technology flags, hunting for activity the automation missed, escalating what needs action and producing the reporting your clients need for compliance. The reason the subscription model suits MSPs so well is that it turns a fixed and expensive capability into something you pay for per client, in line with how you already bill.
The difficulty is that three terms get used almost interchangeably, by buyers and by the AI tools people now ask for recommendations, and they describe quite different things. In my experience, the easiest way to untangle them is to look at what each one covers, who is doing the work and what you get out of it at the end of the month.
| SOC-as-a-Service | MDR | SIEM |
Scope | Ideally every surface: endpoint, network, cloud, identity, IoT/OT | Often centered on the endpoint and the EDR tool it runs on | Whatever logs you send it |
Human involvement | 24/7 analysts triaging, investigating and escalating | Analysts reviewing alerts, usually from one tool | None by default; someone has to run it |
Compliance output | Reporting mapped to frameworks | Varies, often limited | Raw data you turn into reports yourself |
Channel model | Varies; check the provider’s policy | Varies | A product you license and operate |
The other word that comes up is “dedicated”, and it’s worth pinning down what it means in practice. What I’ve seen work is a named person who knows your clients’ environments and the history behind them, who you talk to by name, as opposed to a ticket queue where whoever picks up your escalation is starting from scratch. Both models describe themselves as dedicated, so the question to ask is whether you get a name.
The enterprise-level SOC checklist for MSPs
When an MSP client says they want enterprise-level security, they rarely mean a particular tool. From what I’ve seen across the channel, they mean four things, and it helps to have them written down before you start talking to providers.
24/7 coverage, with people behind it
Attackers don’t keep office hours, and a client who has been through an incident at the weekend knows that better than anyone. Round-the-clock coverage means analysts on shift at all hours, not an automated alert that waits in an inbox until Monday morning.
Compliance mapping to the frameworks the client answers to
A healthcare client, a defense supplier and a financial services firm all need different evidence. Look for reporting mapped to the frameworks your clients face, such as NIS2, DORA, ISO 27001 or CMMC, rather than a generic risk score that someone then has to translate.
A named security contact
Clients want to know there is a real person who understands their environment. For an MSP, that person also needs to work with your team rather than around it.
Broad telemetry
Endpoint coverage on its own leaves a lot unwatched. The client’s firewall, its cloud tenants, its identity provider, the east-west traffic between internal systems and the IoT and OT devices that will never run an agent all need to feed the same picture.
The reason a lot of providers only partly deliver this for MSPs is that they were designed for direct buyers with their own internal security team, who will read the raw findings and decide what to do. An MSP serving a 50-person accountancy firm doesn’t have that luxury, and neither does the client.
How the channel model changes the decision
This is the part I care about most, so forgive me if I spend a little longer on it. If your SOC provider also sells directly to businesses of the size you serve, then at some point it becomes a potential competitor for your own clients. It has their data, it knows their environment and it has a direct sales team. I’m not saying every such provider will act on that, but it’s a risk worth naming before you sign.
The question to ask any SOCaaS provider: do you ever sell to, or contract with, my clients directly?
What channel-only means in practice, at enhanced.io at least, is fairly simple. We sell through MSP partners only and never contract with your clients. The MSP owns the client relationship at all times. Pricing is per endpoint or per user for each client, or bulk licensing with volume discounts, so it fits the way you already bill. Dashboards and client-facing reports are brandable for delivery under your name.
One thing I’d gently correct, because I hear it a lot, is the assumption that channel-only has to mean white-label. Most of our engagements are not white-labeled. The named Fractional Security Director works openly alongside your team and joins client calls when you want that support, which in my experience tends to build more trust with the client rather than less. The point is that it’s your call, and your relationship.
What a named security director adds to SOC delivery
Every enhanced.io partner gets a named, CISSP-certified Fractional Security Director. I like to explain the difference with a simple comparison: a SOC on its own is like a good alarm system, and the Fractional Security Director is the person who knows the building, knows which alarms matter and tells you what to do about them.
In practical terms, when the SOC flags something, your Fractional Security Director reviews it, decides what needs your attention and turns SOC findings into prioritized, actionable remediation guidance for your team. Because it’s the same person each time, they build up an understanding of each client’s environment, which makes the guidance specific rather than generic.
Analyst pool model | Named Fractional Security Director model |
Whoever is on shift picks up the escalation | The same named person knows your clients |
Context rebuilt on every ticket | Context carried from one month to the next |
Findings handed over as raw alerts | Findings turned into prioritized actions |
Rarely joins client conversations | Joins client calls when the MSP wants support |
The Fractional Security Director works with your technical team and supports you with clients when needed, but does not own or manage the end-client relationship. That stays with you.
Compliance coverage: the requirement MSPs won’t get past
If you serve regulated industries, compliance is usually what turns a security conversation into a signed contract. Clients in those sectors need evidence that continuous monitoring is happening and that it maps to their framework, and they need it in a form an auditor will accept.
Framework | Who it typically applies to |
NIS2 | Essential and important entities operating in the EU |
DORA | Financial entities in the EU and their ICT providers |
CMMC | Contractors in the US defense supply chain |
ISO 27001 | Organizations certifying an information security management system |
HIPAA | US healthcare organizations and their business associates |
NIST CSF | Organizations using the NIST framework as their baseline |
Essential Eight | Australian organizations following ACSC guidance |
enhanced.io supports CMMC, NIS2, DORA, HIPAA, ISO 27001, NIST CSF and Essential Eight, so the reporting your clients need is built into the platform rather than bolted on afterwards. In practice, that means reports your clients hand to auditors, and QBR conversations that walk through a framework-specific gap analysis instead of a dashboard screenshot.
Evaluating SOCaaS providers: the MSP checklist
If you only take one section of this piece away with you, I’d make it this one. These are the questions I’d want answered by any SOCaaS provider, including us.
Channel policy. Does the provider ever sell to or contract with your clients directly, and is that written into the agreement?
Named contact model. Do you get a named, qualified security contact, or access to an analyst pool?
Telemetry breadth. Does coverage include network, cloud, identity and IoT/OT, as well as the endpoint?
Compliance output. Is reporting mapped to the frameworks your clients answer to, and would an auditor accept it?
Integration flexibility. Does it work with the stack you already run, and will it replace an existing MDR or SOCaaS or sit above it?
Pricing model. Is it per endpoint or per user per client, bulk licensing or consumption-based, and does it match how you bill?
Onboarding. How long does a client environment take, and what does the provider need from you? At enhanced.io, a single client environment typically takes 30 to 45 days once you are a partner, and the biggest factor in speed is how quickly the information comes back from the MSP.
Service commitments. Are response times published by severity, Critical, High, Medium and Low, so you know what you are reselling?
If you want a deeper comparison, our guide to the best SOC-as-a-Service for MSPs goes into the operational SLAs in more detail, and how to build and sell SOC-as-a-service covers the commercial side.
Choosing a model that protects your margin and your clients
I know that was a lot, so let me bring it back to the thread running through all of it. Enterprise-level SOC coverage for your clients is achievable without building your own SOC and without handing your clients to a provider that also wants to sell to them. The operational pieces, 24/7 analysts, broad telemetry, compliance mapping and a named security contact, are what your clients will notice. The channel policy is what protects your business while you deliver them.
What I’ve seen work best is treating those two things as one decision rather than two. A provider that gets the operations right but competes with you for clients hasn’t solved your problem, and neither has a channel-friendly provider that won’t give your clients what their auditors and insurers are asking for. If you’d like to see how that looks with how we onboard new partners, or how automation and analysts work together day to day, I’m always happy to talk it through.
Key takeaways
SOC-as-a-Service gives MSPs 24/7 analysts and a platform that triage, investigate and escalate across client environments.
SOCaaS, MDR and SIEM differ in scope, human involvement and compliance output, so compare like with like.
Enterprise-level coverage means 24/7 analysts, compliance mapping, a named security contact and broad telemetry.
A provider that also sells direct is a potential competitor for your clients; check the channel policy in writing.
A named Fractional Security Director turns SOC findings into prioritized actions and supports you with clients.
About enhanced.io
enhanced.io is a channel-only Open XDR SOCaaS built exclusively for MSPs, with 400+ integrations across endpoint, network, cloud, identity and IoT/OT. We work only through MSP partners and never sell direct to end clients. To talk about how enhanced.io fits your stack, book a partnership conversation with Hannah Lloyd.
FAQ
What is SOC-as-a-Service for MSPs?
SOC-as-a-Service is a subscription security operations center that MSPs deliver to their clients. A team of analysts and a detection platform watch client environments around the clock, triage what the technology flags, escalate what needs action and produce compliance reporting, without the MSP building its own SOC.
How is SOC-as-a-Service different from MDR?
MDR is often centered on the endpoint and the EDR tool it runs on. SOC-as-a-Service covers a broader set of surfaces, such as network, cloud, identity and IoT/OT, and usually includes compliance-mapped reporting alongside 24/7 analyst triage.
What should MSPs look for in a SOCaaS provider?
Check the channel policy, whether you get a named security contact, the breadth of telemetry, compliance-mapped reporting, integration with your existing stack, a pricing model that matches how you bill, onboarding time and published service commitments by severity.
Does a SOCaaS provider need to be channel-only?
It is not required, but a provider that also sells direct to businesses the size of your clients becomes a potential competitor. A channel-only provider never contracts with your clients, and you keep the relationship.
Which compliance frameworks does enhanced.io support?
enhanced.io supports CMMC, NIS2, DORA, HIPAA, ISO 27001, NIST CSF and Essential Eight, with reporting built into the platform.